[NEW!] Introducing AVA Agentic OS

CTEM Runs on AVA Agentic OS

AVA OS is the operating system for CTEM, orchestrating specialized AI agents that execute autonomous cybersecurity missions to continuously validate defenses, break attack paths, and reduce threat debt.

Request a Demo See AVA OS in Action

Every Assumption Is Now a Vulnerability

AI compresses the time between exposure and exploitation. Disconnected tools and point-in-time security assessments can’t keep pace.

AttackIQ defends at AI speed, turning threat intelligence, exposure data, and adversary emulation into a closed-loop system where findings drive validation and fixes become measurable progress.

You Don’t Catalog Assets.

You See Like
an Adversary

Map the assets, identities, and threats that shape your environment

You Don’t Chase Findings.

You Break Attack Paths

Pinpoint the exposures that create viable routes to critical systems

You Don’t Assume Coverage.

You Prove
It Works

Validate controls against the techniques adversaries actually use

You Don’t Report Activity.

You Reduce Threat Debt

Continuously break the attack paths that put your business at risk

Explore the CTEM Platform

Threat Debt Index

Prove Attacker Opportunity Is Going Down

The AttackIQ Threat Debt Index™ gives teams and leadership a single view of exploitable opportunity over time: current balance, what was reduced, and what has newly accrued as conditions changed.

It reports outcomes, not activity, so you can prove progress, not just claim it.

What Is Threat Debt?

Built for the Way CTEM Actually Works

CTEM is the framework. AttackIQ turns it into results you can measure.

Exposure Management

Not Every Exposure Creates Risk

Which ones actually put the business at risk?

Most exposure lists are ranked by severity, with noise. AttackIQ prioritizes based on attacker reach, business impact, and validated exploitability, so teams focus on the paths that pose meaningful risk

Reduce Exposure

Detection Engineering

Your Detections Have Gaps

You just can’t see them yet

Map detection coverage to how attacks actually operate. Tune what adversaries exploit, not just what generates the most alerts

Improve Detection

Security Control Validation

Deployed Doesn’t Mean Effective

Are your controls stopping attacks or failing silently?

Validate whether controls block, detect, alert, and escalate against adversary techniques across your environment

Validate Controls

Offensive Testing

Point-In-Time Tests Don’t Hold

How do you know what still works?

Execute full attack paths across identity, cloud, endpoint, and network environments continuously, not occasionally

Run Offensive Testing

What CTEM Done Right Looks Like

Threat Debt Index

Pay Down Rate

Mean Time to Detect (MTTD)

45% Faster, in 90 Days

MITRE ATT&CK Coverage

Tested Against Techniques That Matter Most

Operationalize CTEM

CTEM In
90 Days

Go from scoping to mobilization, fully operational in 90 days.

Start CTEM in 90 Days

Smarter Security,
Proven Results

Gain unparalleled visibility, efficiency, and control for unmatched protection,
cost savings, and peace of mind.

0
Lower Breach Costs
0
Faster Security Operations
0
Higher SOC Analyst Output
0
Reduced Tool Sprawl

Real Impact for Real-World
Security Challenges

From Fortune 500 companies to mid-sized enterprises, organizations across industries trust us to keep them resilient.

  • “Even before working with AttackIQ, we were basing our pen testing decisions and our metrics on the MITRE ATT&CK framework. The tight integration of MITRE ATT&CK principles into the Security Optimization Platform is one of the things we liked about AttackIQ from the beginning.”
    Senior Full-Stack Software Developer
    Case Study: ESED
  • Banking

    5 Star Review “The journey we started was great because the AttackIQ staff were there to help us adopt the product as easily as possible. Definitely consider the use of AttackIQ, the insights and regular reporting it will provide will only benefit your organization.”
    Information Security Specialist
    Gartner Peer Insights
  • Facility Management Services

    “AttackIQ enables us to be more strategic with our security investments. What should we implement next to drive down risk? Automation is a smarter way of answering that question than manual pen testing because it reduces the cost of testing and increases the thoroughness of assessments. It plays a crucial role in our security investment decisions”
    Chief Information Security Officer (CISO)
    ISS World Services A/S, One of the World’s Leading Facilities Management Providers, Finds Efficient Road to Security Visibility
  • Banking

    5 Star Review Overall experience with the product is great! The product has provided so much insight into our systems and has allowed improvement of overall security posture. Product can be in the high end in terms of pricing but it is money well spent! Regular updates of the attack library and the ability to customize it to your needs. Very simple to use.
    Information Security Specialist
    Gartner Peer Insights
  • Retail

    “What the Security Optimization Platform enables me to do is to demonstrate to our CISO, other senior leadership, and the board that we are doing the right thing. I’m not just saying it; I have evidence that proves it. I can run a test and show them exactly how our systems and teams respond. That capability is invaluable with an attack surface as broad and complex as ours.”
    Director of Security Operations
    Building Confidence in Security Effectiveness Across a Fortune 500 Retailer’s Complex Global Infrastructure
  • Insurance

    “AttackIQ has done wonders in terms of giving us a clear picture. One CISO responded to the results of a test and said, ‘I don’t believe this.’ We got some engineers to perform an independent validation and, sure enough, the AttackIQ results were correct. Having assessment data at my fingertips is very useful when I need to push a team to take certain actions.”
    Director of Information Security
    Major General Insurer Boosts Cybersecurity Readiness Across a Broad and Diverse Infrastructure
  • Facility Management Services

    “We might see, hypothetically, that we’re good on protecting against ‘initial foothold’ with a particular type of malware, but we are not doing well in protecting data on a certain type of device from being exfiltrated. We can use that information to understand what we need to change. Maybe we see that we are preventing the first five steps of the attack, so it’s unlikely that an attacker will get to the sixth step, where we might have a gap. Using the MITRE framework to break down attacks like this helps us decide where to invest additional resources.”

    Global Information Security Manager
    ISS World Services A/S, One of the World’s Leading Facilities Management Providers, Finds Efficient Road to Security Visibility
  • “Even before working with AttackIQ, we were basing our pen testing decisions and our metrics on the MITRE ATT&CK framework. The tight integration of MITRE ATT&CK principles into the Security Optimization Platform is one of the things we liked about AttackIQ from the beginning.”

    Senior Full-Stack Software Developer
    Case Study: ESED
  • Retail

    “What the Security Optimization Platform enables me to do is to demonstrate to our CISO, other senior leadership, and the board that we are doing the right thing. I’m not just saying it; I have evidence that proves it. I can run a test and show them exactly how our systems and teams respond. That capability is invaluable with an attack surface as broad and complex as ours.”

    Director of Security Operations
    Building Confidence in Security Effectiveness Across a Fortune 500 Retailer’s Complex Global Infrastructure
  • Defense, Transportation

    “I run AttackIQ on my systems every two weeks. The AttackIQ Security Optimization Platform is central to my routine testing process, checking vulnerabilities I know about and looking for new ones. AttackIQ gives us instantaneous results when a scenario has finished running. That means we find out about problems and get them fixed months sooner than when we were using an external red team. AttackIQ shrunk our response time for zero-day threats from days to hours. That has been really helpful to our business.”

    Senior Information Security Analyst and Security Tester
    U.S. Defense Contractor Harnesses AttackIQ to Improve Customers’ Operational Readiness
  • Security

    “We’ve had a lot of success with the AttackIQ Security Optimization Platform across client engagements, internal training, and also in identifying opportunities to further apply threat-informed defense in our own environment. These simulated attacks that are aligned to the organization’s customized threat model generates visibility into the effectiveness of their controls for a threat-informed defensive posture. The platform is an important tool for our business and a key component of our value proposition.”

    Managing Director
    The Chertoff Group Leverages AttackIQ Security Optimization Platform to Deliver Compelling Security Service for Clients
  • Retail

    “In a lot of ways, the comprehensiveness and complexity of the security architecture we’ve built is driving our need for the AttackIQ tool — we need an external capability to see that what we expect to be protected is actually being protected.”

    Director of Security Operations
    Building Confidence in Security Effectiveness Across a Fortune 500 Retailer’s Complex Global Infrastructure

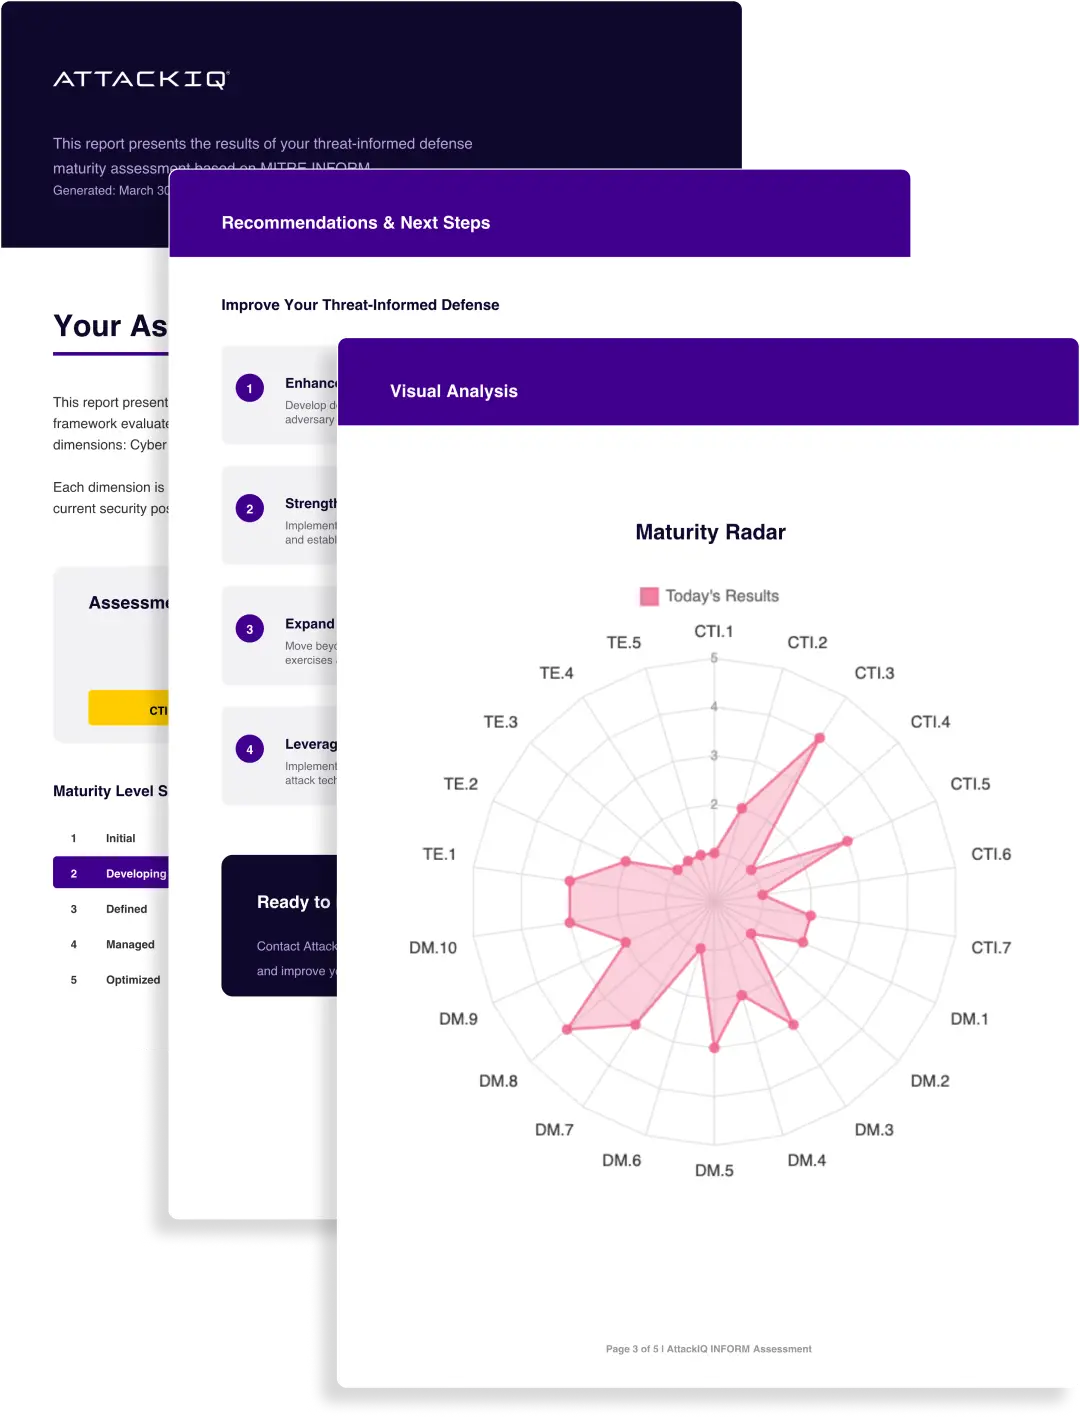
How Threat-Informed Is Your Defense, Really?

MITRE ATT&CK tells you how attackers operate. This tells you if your program is ready.

Benchmark your defense in minutes. Get a scored breakdown across CTI, Defensive Measures, Testing, and CTEM — with prioritized recommendations so you know what to fix first.
Take the Free Assessment

Featured Articles

  • CTEM + MITRE INFORM For Dummies

    This new For Dummies guide explains how Continuous Threat Exposure Management (CTEM) and MITRE INFORM work together to establish a continuous, measurable approach to cyber resilience, grounded in operational performance and real-world evidence.
    Read More
  • The AI Vulnerability Storm

    Anthropic reveals AI that autonomously discovers and exploits vulnerabilities at scale. This shift reshapes cyber risk—learn what it means and what to do.
    Read More
  • Threat Debt: The Unit of Measure Adversaries Already Use Against You

    Threat debt measures the exploitable attack paths adversaries can actually use. Learn how the Threat Debt Index helps security teams prioritize remediation, reduce exposure, and prove risk reduction.
    Read More