[NEW!] Introducing AVA Agentic OS

CTEM Runs on AVA Agentic OS

AVA OS is the operating system for CTEM, orchestrating specialized AI agents that execute autonomous cybersecurity missions to continuously validate defenses, break attack paths, and reduce threat debt.

Request a Demo See AVA OS in Action

Every Assumption Is Now a Vulnerability

AI compresses the time between exposure and exploitation. Disconnected tools and point-in-time security assessments can’t keep pace.

AttackIQ defends at AI speed, turning threat intelligence, exposure data, and adversary emulation into a closed-loop system where findings drive validation and fixes become measurable progress.

You Don’t Catalog Assets.

You See Like
an Adversary

Map the assets, identities, and threats that shape your environment

You Don’t Chase Findings.

You Break Attack Paths

Pinpoint the exposures that create viable routes to critical systems

You Don’t Assume Coverage.

You Prove
It Works

Validate controls against the techniques adversaries actually use

You Don’t Report Activity.

You Reduce Threat Debt

Continuously break the attack paths that put your business at risk

Explore the CTEM Platform

Threat Debt Index

Prove Attacker Opportunity Is Going Down

The AttackIQ Threat Debt Index™ gives teams and leadership a single view of exploitable opportunity over time: current balance, what was reduced, and what has newly accrued as conditions changed.

It reports outcomes, not activity, so you can prove progress, not just claim it.

What Is Threat Debt?

Built for the Way CTEM Actually Works

CTEM is the framework. AttackIQ turns it into results you can measure.

Exposure Management

Not Every Exposure Creates Risk

Which ones actually put the business at risk?

Most exposure lists are ranked by severity, with noise. AttackIQ prioritizes based on attacker reach, business impact, and validated exploitability, so teams focus on the paths that pose meaningful risk

Reduce Exposure

Detection Engineering

Your Detections Have Gaps

You just can’t see them yet

Map detection coverage to how attacks actually operate. Tune what adversaries exploit, not just what generates the most alerts

Improve Detection

Security Control Validation

Deployed Doesn’t Mean Effective

Are your controls stopping attacks or failing silently?

Validate whether controls block, detect, alert, and escalate against adversary techniques across your environment

Validate Controls

Offensive Testing

Point-In-Time Tests Don’t Hold

How do you know what still works?

Execute full attack paths across identity, cloud, endpoint, and network environments continuously, not occasionally

Run Offensive Testing

What CTEM Done Right Looks Like

Threat Debt Index

Pay Down Rate

Mean Time to Detect (MTTD)

45% Faster, in 90 Days

MITRE ATT&CK Coverage

Tested Against Techniques That Matter Most

Operationalize CTEM

CTEM In
90 Days

Go from scoping to mobilization, fully operational in 90 days.

Start CTEM in 90 Days

Smarter Security,
Proven Results

Gain unparalleled visibility, efficiency, and control for unmatched protection,
cost savings, and peace of mind.

0
Lower Breach Costs
0
Faster Security Operations
0
Higher SOC Analyst Output
0
Reduced Tool Sprawl

Real Impact for Real-World
Security Challenges

From Fortune 500 companies to mid-sized enterprises, organizations across industries trust us to keep them resilient.

  • Fortune 50 Retailer

    “Our initial intention is to ensure whatever endpoint security solution we have, that our technology stack is firing appropriately. That it’s catching when it’s supposed to catch, preventing what’s supposed to prevent. AttackIQ has allowed us to test and get a good picture of our EDR capabilities. I know AttackIQ is working as intended because the detections have increased. We are up around 30% for our detections.”
    Lead Information Security Analyst, Offensive Security Group
    A Fortune 50 Retailer Relies on AttackIQ for Automated Security Control Validation Against Real World Threats
  • Biosciences

    “We leveraged AttackIQ for breach and attack simulations against our incumbent XDR provider. There was cost saving involved because we were able to demonstrate that our existing solution was more effective than these much more expensive alternatives that came to the table with many promises. Based on our AttackIQ results, we could maintain that existing vendor relationship, and it’s been successful.”
    Director of IT Security
    Leading Biosciences Company Demonstrates Security Control Effectiveness and Reduces Insurance Premiums Using AttackIQ
  • Biosciences

    “AttackIQ was really the best of breed. There was no question that it was the right choice for us after leveraging the free resources through the Academy. AttackIQ is invested in the community and expanding the knowledge to cybersecurity professionals. There’s much value and integrity in that. I look forward to this in partnerships. We leverage AttackIQ Academy as an onboarding process for new hires. Both current analysts have gone through every training module and certification. It’s a great training resource. Finding a solution like AttackIQ, where we can train our existing staff and augment the need for full-time red team practitioners on board, is huge.”
    Director of IT Security
    Leading Biosciences Company Demonstrates Security Control Effectiveness and Reduces Insurance Premiums Using AttackIQ
  • Fortune 500 Asset Management Firm (Finance)

    “At first it was difficult to maintain the cadence of operations as people took to their home offices. However, with AttackIQ, we had a platform that could continue the same levels of automated testing regardless of what was going on around it. That helped us establish a strong baseline and understand what was happening to key controls during this chaotic period.”
    Red Team Leader
    Fortune 500 Asset Management Firm Empowers its Purple Team with the AttackIQ Security Optimization Platform
  • Insurance

    “They might think they’ve successfully closed a control gap. We can prove whether that’s true; we don’t have to take their word for it. Without AttackIQ, it would be possible for my team to do that, but it would be extremely time-consuming. They would have to reach out to the end user support team, get a machine on the network in question, then run the attack and see whether it succeeds. With Attack IQ, we just push a button to re-run the test that revealed the problem in the first place.”
    Director of Information Security
    Major General Insurer Boosts Cybersecurity Readiness Across a Broad and Diverse Infrastructure
  • Fortune 50 Retailer

    Now, we can automatically test something and get feedback within the AttackIQ. Nobody needs to check for alerts manually. We brought automated testing to different teams, like for our blue and networking teams, for networking segmentation.
    Lead Information Security Analyst, Offensive Security Group
    A Fortune 50 Retailer Relies on AttackIQ for Automated Security Control Validation Against Real World Threats
  • Fortune 50 Retailer

    “MITRE ATT&CK has been an enormous resource for us. We use it a lot with AttackIQ because we aren’t just concentrating on our EDR baselines. But there are known TTPs that specifically target similar industries to us. We use the MTIRE ATT&CK framework to determine what to go after and what to test next.”

    Lead Information Security Analyst, Offensive Security Group
    A Fortune 50 Retailer Relies on AttackIQ for Automated Security Control Validation Against Real World Threats
  • Banking

    5 Star Review Overall experience with the product is great! The product has provided so much insight into our systems and has allowed improvement of overall security posture. Product can be in the high end in terms of pricing but it is money well spent! Regular updates of the attack library and the ability to customize it to your needs. Very simple to use.

    Information Security Specialist
    Gartner Peer Insights
  • Facility Management Services

    “It helps me provide detailed reports to the C-suite, the board, and auditors to create transparency around our return on investment as a corporate security function. There are still a lot of things that keep me up at night, but I am sleeping much better now than I did before we started working with AttackIQ.”

    Chief Information Security Officer (CISO)
    ISS World Services A/S, One of the World’s Leading Facilities Management Providers, Finds Efficient Road to Security Visibility
  • Facility Management Services

    “The AttackIQ platform greatly accelerates the threat mitigation process. Instead of waiting a month for a penetration test to be completed, we can do it all in one combined workshop. It saves time and money. We saw the opportunity to automate and run all sorts of attacks and techniques through it. We knew we could dramatically improve visibility into our security effectiveness, and be more efficient with our team resources.”

    Global Information Security Manager
    ISS World Services A/S, One of the World’s Leading Facilities Management Providers, Finds Efficient Road to Security Visibility
  • Banking

    The journey we started was great because the AttackIQ staff were there to help us adopt the product as easily as possible. Definitely consider the use of AttackIQ, the insights and regular reporting it will provide will only benefit your organization.

    Information Security Specialist
    Gartner Peer Insights
  • Defense, Transportation

    “I run AttackIQ on my systems every two weeks. The AttackIQ Security Optimization Platform is central to my routine testing process, checking vulnerabilities I know about and looking for new ones. AttackIQ gives us instantaneous results when a scenario has finished running. That means we find out about problems and get them fixed months sooner than when we were using an external red team. AttackIQ shrunk our response time for zero-day threats from days to hours. That has been really helpful to our business.”

    Senior Information Security Analyst and Security Tester
    U.S. Defense Contractor Harnesses AttackIQ to Improve Customers’ Operational Readiness

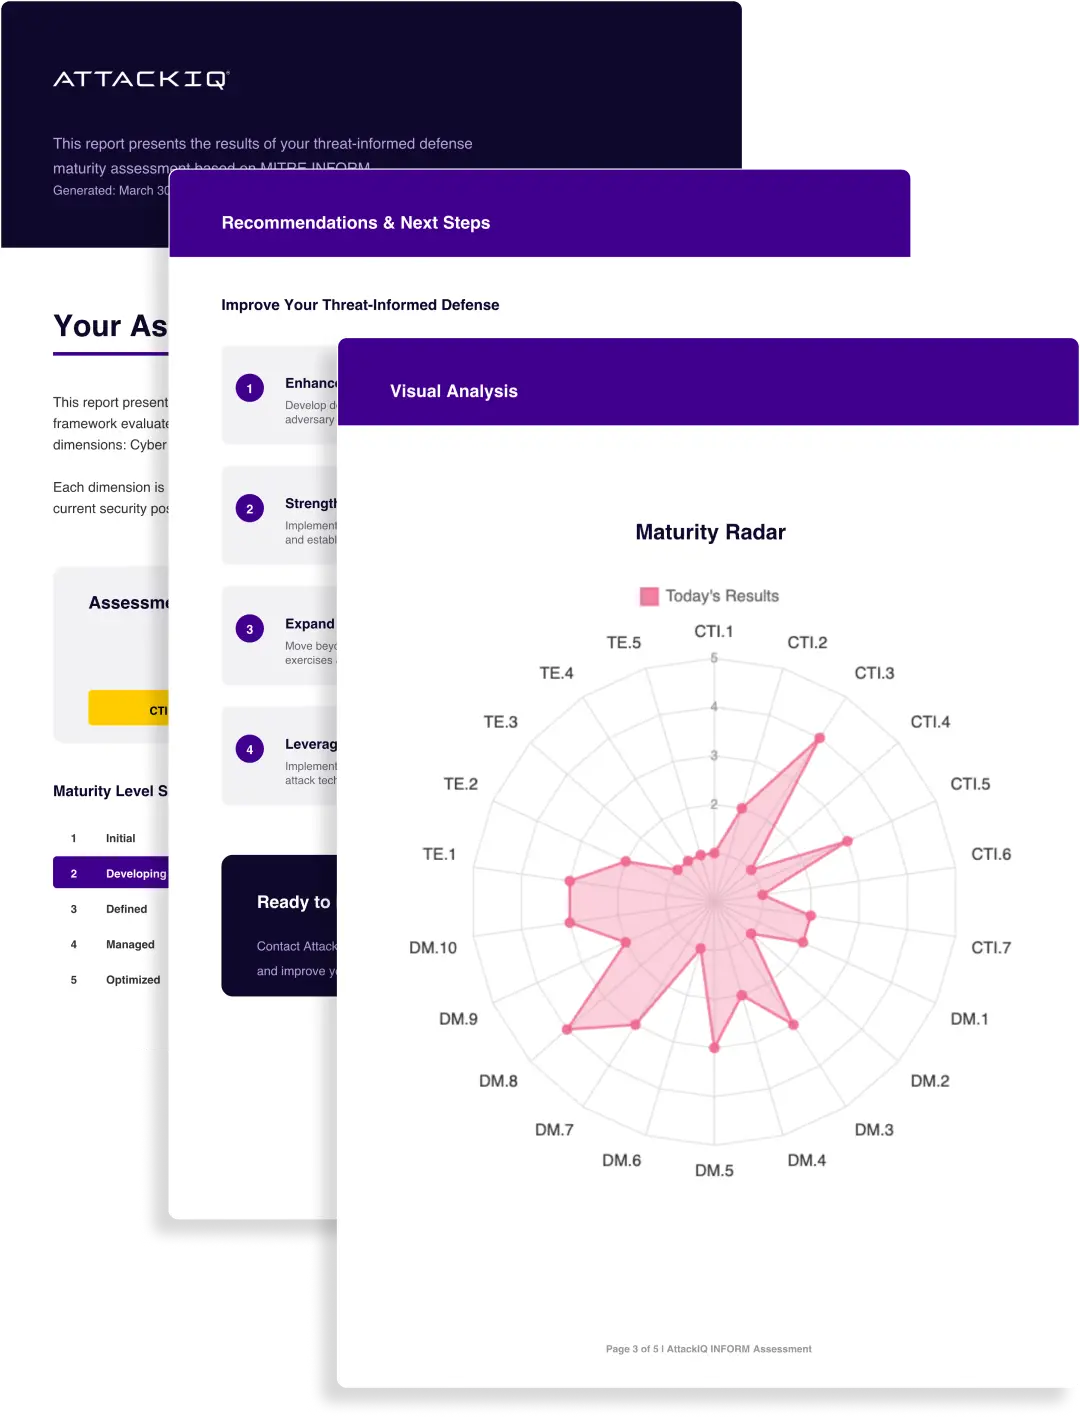
How Threat-Informed Is Your Defense, Really?

MITRE ATT&CK tells you how attackers operate. This tells you if your program is ready.

Benchmark your defense in minutes. Get a scored breakdown across CTI, Defensive Measures, Testing, and CTEM — with prioritized recommendations so you know what to fix first.
Take the Free Assessment

Featured Articles

  • CTEM + MITRE INFORM For Dummies

    This new For Dummies guide explains how Continuous Threat Exposure Management (CTEM) and MITRE INFORM work together to establish a continuous, measurable approach to cyber resilience, grounded in operational performance and real-world evidence.
    Read More
  • The AI Vulnerability Storm

    Anthropic reveals AI that autonomously discovers and exploits vulnerabilities at scale. This shift reshapes cyber risk—learn what it means and what to do.
    Read More
  • Threat Debt: The Unit of Measure Adversaries Already Use Against You

    Threat debt measures the exploitable attack paths adversaries can actually use. Learn how the Threat Debt Index helps security teams prioritize remediation, reduce exposure, and prove risk reduction.
    Read More